What Is Zero Trust Architecture and How Does It Work?
Firms are now becoming reliant on cloud computing, remote access, devices, and distribution networks for conducting their business transactions. Although these tools make it easy to operate and perform tasks effectively, they create an increased potential for cyber threats. The conventional security system that considers any user inside the organization’s network as trustworthy might fail to guard against compromised credentials, insider attacks, or any other form of breach.
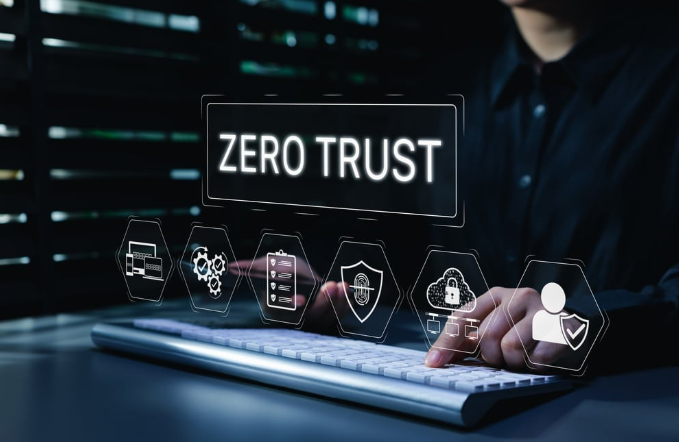
The Zero Trust Architecture is an alternative solution that involves verifying all requests for access, regardless of whether they come from the organization’s network or not. This architecture is based on identity verification, access policy, secure devices, and monitoring to make sure that these resources are protected. Having more knowledge regarding the Zero Trust Architecture may be advantageous for organizations.
What Is Zero Trust Architecture?
Zero Trust Architecture is a security framework that does not automatically trust users or devices before granting access to resources. Instead, it evaluates the identity of the requester, the security status of the device, the requested resource, and other relevant risk factors before authorizing access. This approach helps organizations enforce consistent security policies and reduce the risk of unauthorized access. A closer look at what is zero trust architecture can help businesses understand its core principles and practical applications.
Core Elements of a Zero Trust Architecture
The elements that need to be incorporated in order to implement Zero Trust architecture effectively include the following security aspects.
1. Identity and Access Management
Through identity management, one determines who wants access and what kind of access is permitted. Multi-factor authentication helps provide an extra security layer; therefore, no one will ever misuse the credentials that they steal.
Role-based access control helps organizations to offer the necessary permissions for their staff members. Organizations should ensure that they cancel those permissions when the employees switch their roles or exit from the organization.
2. Device Security and Validation
Simply verifying the user is not sufficient. Even a legitimate user’s credentials can be exploited by using the account from a compromised or out-of-date device.
Zero Trust checks for security of the device prior to giving access to sensitive assets. Some of the factors that might be evaluated are operating system patches, endpoint validation, device settings, and compliance with organizational policies.
3. Principle of Least Privilege
Under this principle, users and applications should be provided with only the minimum amount of access required to perform their job functions. This principle makes sure that in case of any breach to an account, mistake, or an insider attack, the damage will be kept at a minimum.
In this regard, a marketing professional may be allowed to use campaign tools but not production systems or salary databases.
4. Network Segmentation
Network segmentation involves segmenting the environment to create small manageable compartments. Rather than giving free flow access across systems, companies have put in place rules on how the systems can communicate with each other.
It will prevent attackers who have succeeded in gaining entry to a particular system from having access to other critical systems in the network. Microsegmentation goes even further.
Key Advantages of Zero Trust Architecture in Business Organizations
Zero Trust offers many benefits to companies that require protection of distributed users, applications, and data.
- Access control: High verification and authorization capabilities will reduce the chances of getting access to sensitive data by unauthorized persons.
- Lessened ability to spread threats: Through network segmentation, attack spread can be controlled.
- Enhanced security for remote users: The same verification policies will secure users when they connect from any location.
- Protection of data: Access limitation will ensure less exposure of private company information.
- Better visibility: User and system monitoring will give more insight into user and system actions.
Where Zero Trust Architecture Can Be Applied
There are many places where Zero Trust could be implemented because Zero Trust architecture is centered around protecting resources and does not depend on the location of the network.
1. Cloud Applications and Services
The cloud typically includes applications and data to which access is provided to employees, contractors, and partners. Zero Trust offers security in such an environment through identity, access to workloads, and monitoring.
Permissions need to be defined properly and the cloud infrastructure secured in order to make sure that the access will depend on the context of the request, not on previous sign-ons.
2. Remote and Hybrid Workforces
Remote workforces can be accessed via home networking systems, public WiFi connections, or personal computers. The Zero Trust framework guarantees that there will be equal access control parameters for remote staff, ensuring that businesses will reduce the reliance on network locations.
3. Sensitivity and Control of Environment
Organizations with sensitive information need precise control over who is permitted access to specific files and systems. Zero Trust is capable of helping to ensure such demands through granular permissions, logging and verification.
For example, healthcare cybersecurity best practices help healthcare organizations protect sensitive patient information and manage access to electronic health records. These measures support the broader security objectives of a Zero Trust approach.
See also: Understanding the Process of Establishing an International Business
Zero Trust Architecture Implementation Best Practices
Implementing Zero Trust Architecture is an iterative approach that takes some time to achieve through planning and collaboration. Organizations must focus on their most crucial assets before extending security policies to all assets within the organization.
Start With Asset Visibility
Develop an asset inventory comprising users, devices, applications, services, and any valuable information. Asset inventory will help security teams understand what they are protecting, including dependencies.
Define Clear Access Policies
Identify who can access all the assets within an organization. Make sure the access control policy takes into account the circumstances and reasons for doing so.
Segment Critical Resources
Isolate valuable assets and sensitive applications from noncritical segments. Control communications between segments to those necessary for business needs.
Monitor and Improve Constantly
Generate appropriate security logs, analyze anomalies, and audit access requests. Guidelines on a Zero Trust security approach stress the importance of verification, fine-grained access control, and evaluating users, devices, and resources.
Other activities include testing policies, training staff, and enhancing controls based on business needs and emerging threats.
Common Challenges When Adopting Zero Trust
Even though a Zero Trust approach might improve security, there could be several difficulties during its implementation. Legacy systems may lack modern authentication capabilities, and incomplete asset management may cause difficulties in creating access policies. Businesses could face other problems such as integration issues, increased administrative workload, or dissatisfaction among users.
In order to overcome these difficulties, the company should start from defining scope, prioritizing resources, and rolling out changes gradually. Testing policies on a small sample will help to identify possible configuration difficulties and minimize disruptions. Communication is crucial as well.
Final Thoughts
ZTA represents an evolution in cybersecurity that replaces implicit trust with verification. Leveraging identity and device management, least privilege access, network segmentation, and constant monitoring, a company is able to protect its assets irrespective of a computing environment – whether clouds, remote access, or legacy computing.
The effective implementation of the Zero Trust architecture framework is not just about having certain technologies at one’s disposal but requires a company to have access control policies, know what assets it has, and assess its security processes. A phased approach may prove useful.
FAQ
1. Is Zero Trust Architecture a product or a framework?
Zero Trust Architecture is a security framework and not a product. It is a combination of various technologies and rules which help to protect the resources.
2. Does Zero Trust Architecture replace firewalls?
No. The use of firewalls for managing the traffic on the network is still relevant. With the implementation of Zero Trust Architecture, the identification and authorization of access requests are facilitated.
3. Is Zero Trust Architecture applicable to small businesses?
Yes, it is possible to apply the Zero Trust architecture to small businesses with the use of multi-factor authentication, limiting of users’ permissions, protection of devices and access control.
4. What is the time required for the Zero Trust process implementation?
The time depends on the size of the company, infrastructure and security needs. Companies usually start from the most critical accounts and applications.